Introduction
The CISSP Security Assessment and Testing PDF serves as a vital resource for security professionals. This document encapsulates essential concepts that facilitate efficient security assessments and testing protocols. It aims to educate and prepare individuals for the ever-evolving landscape of cybersecurity.
Overview about the Document
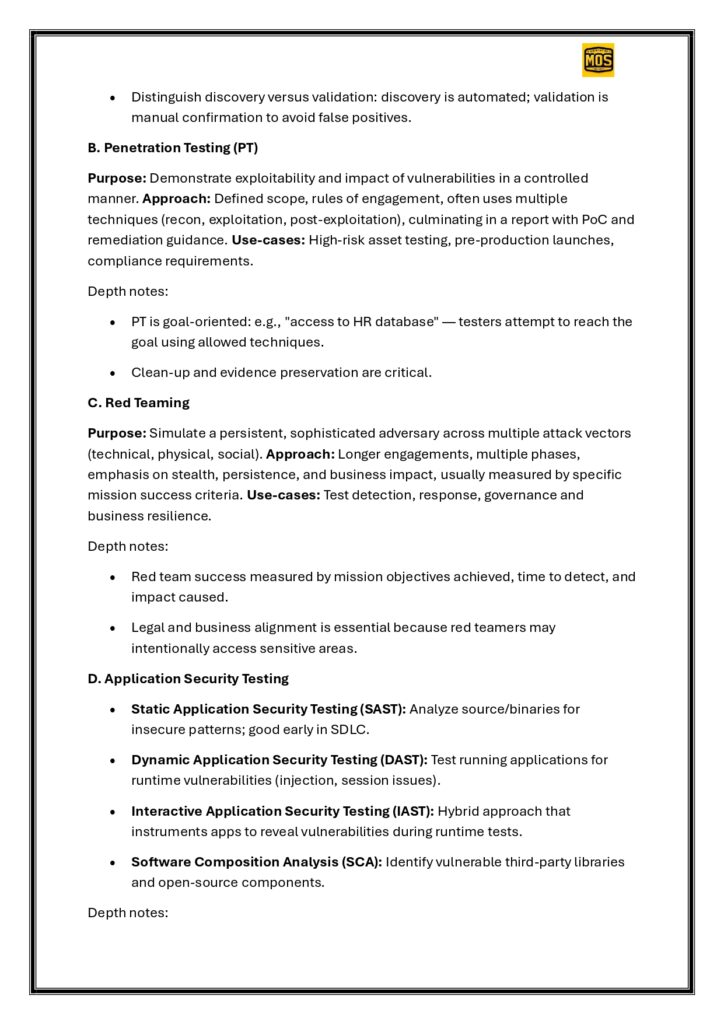
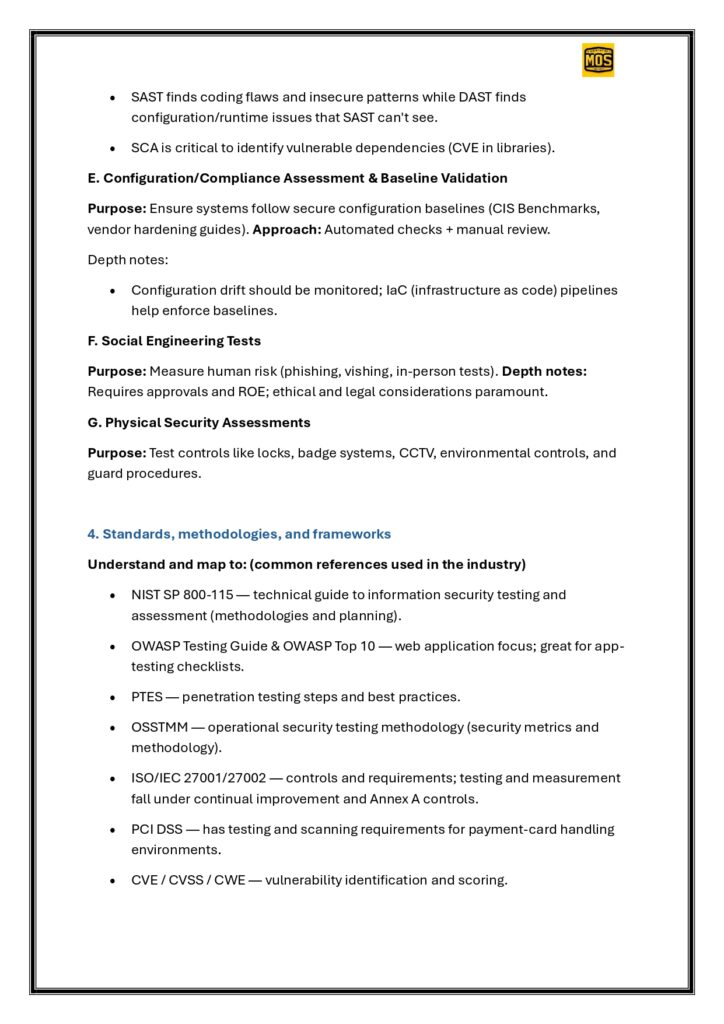
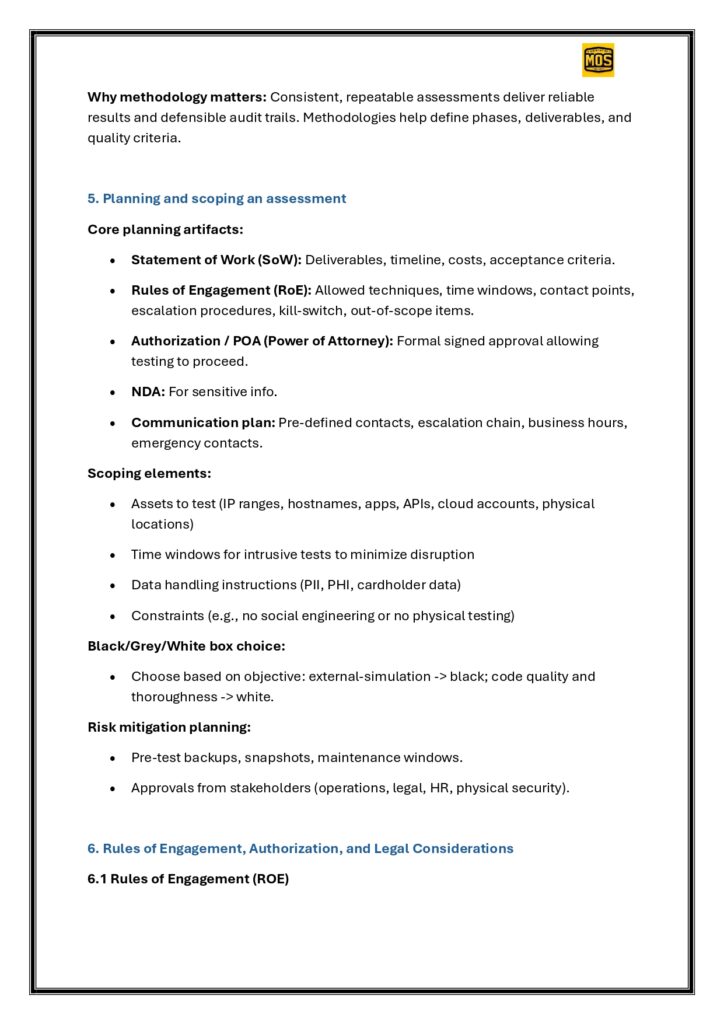
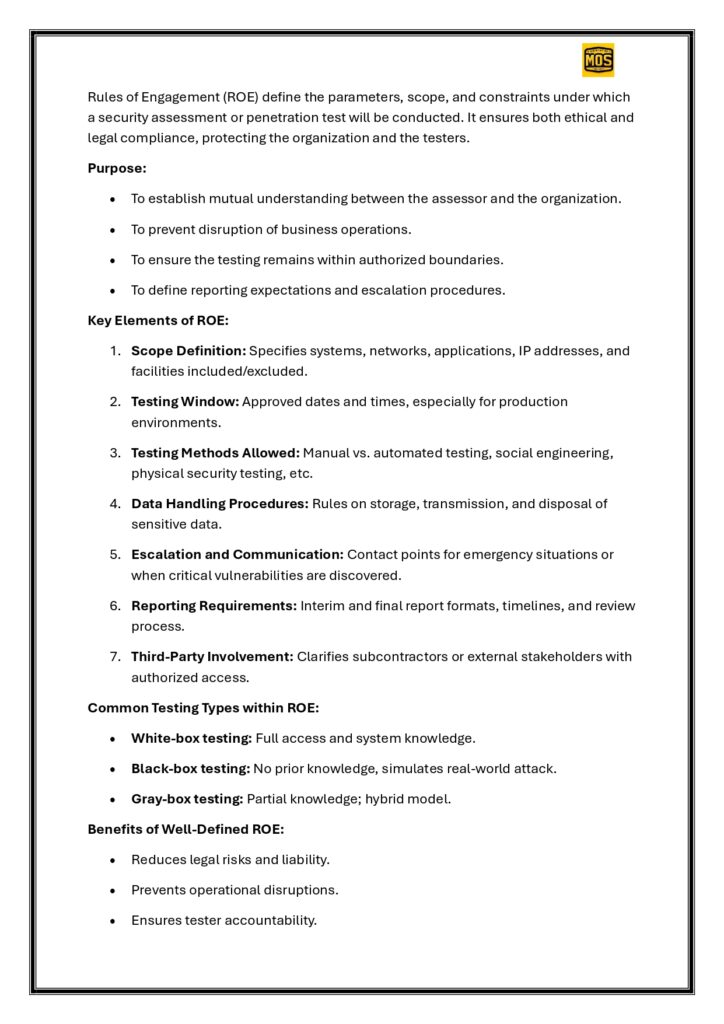
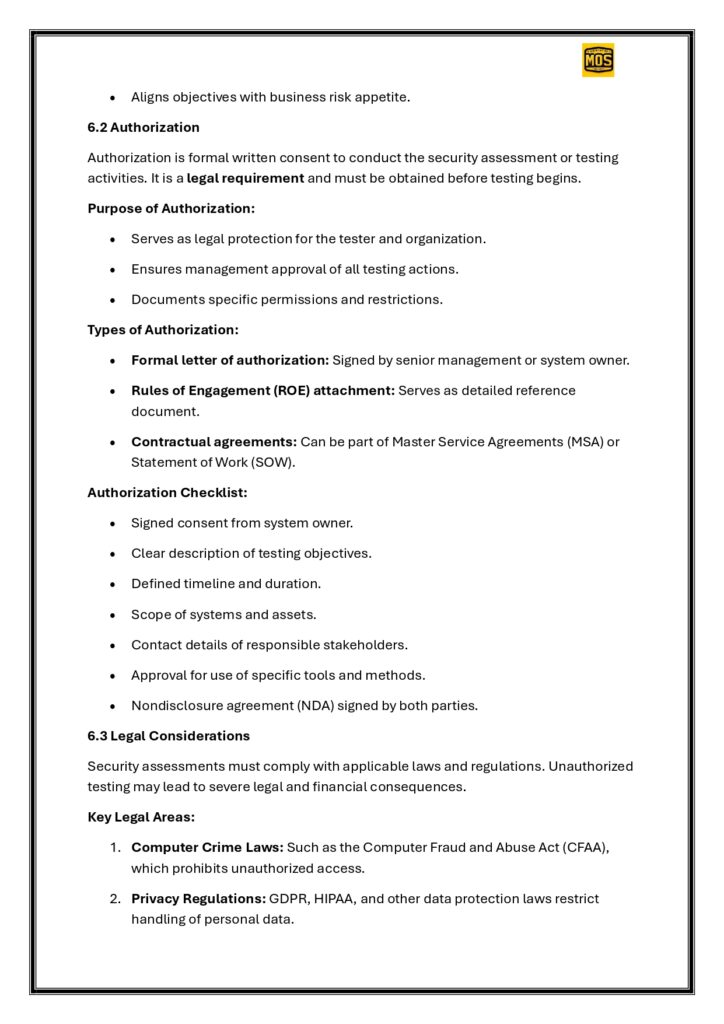
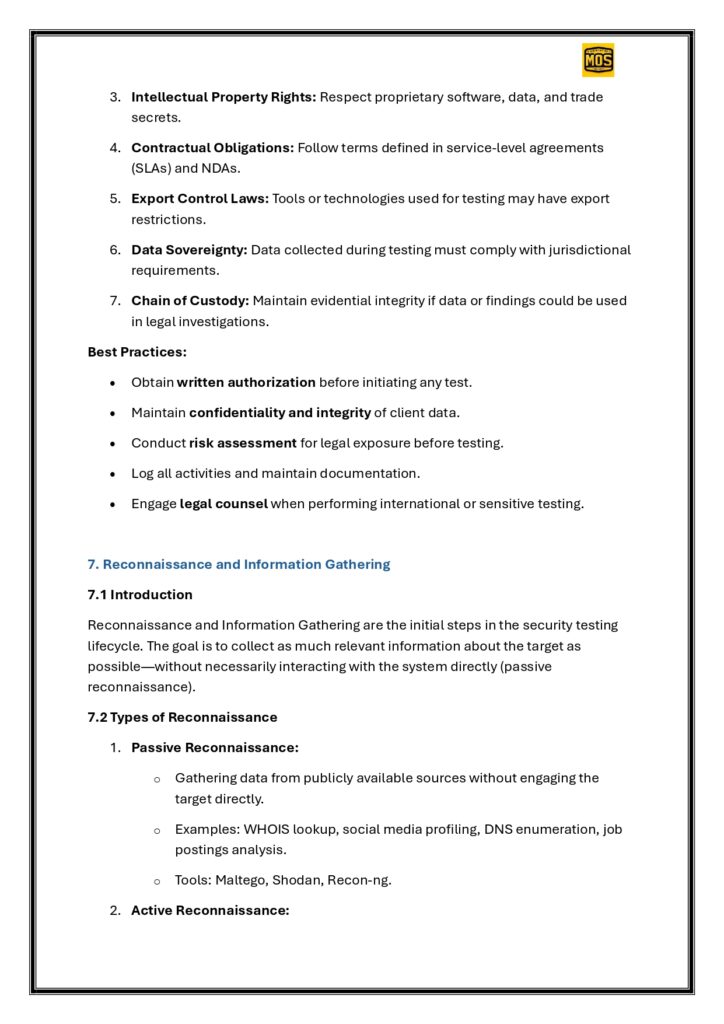
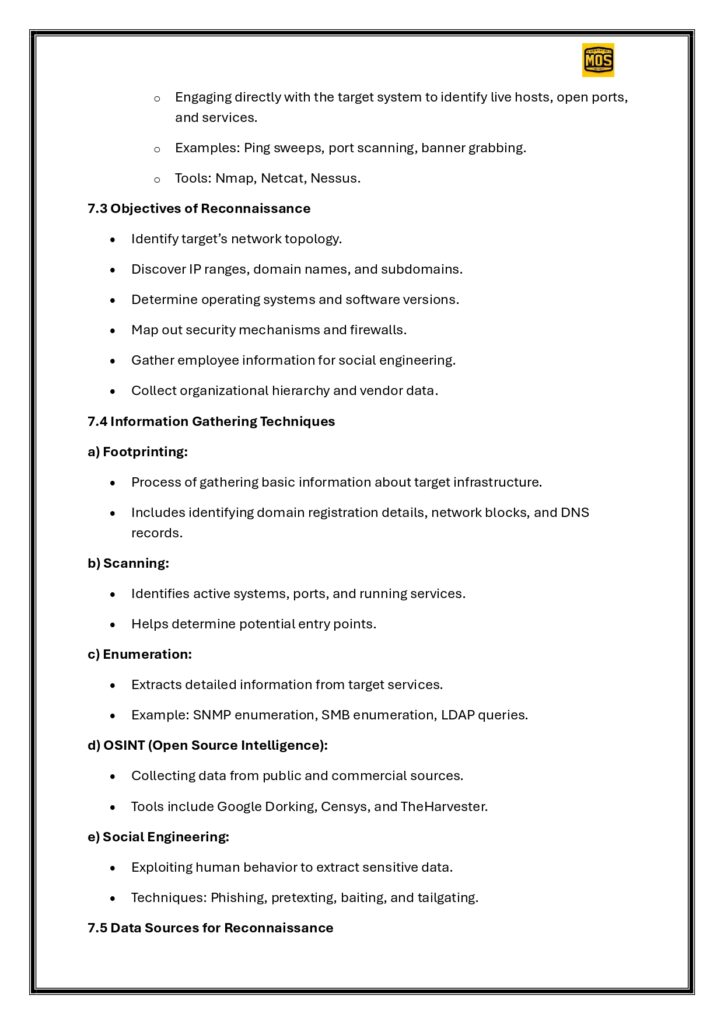
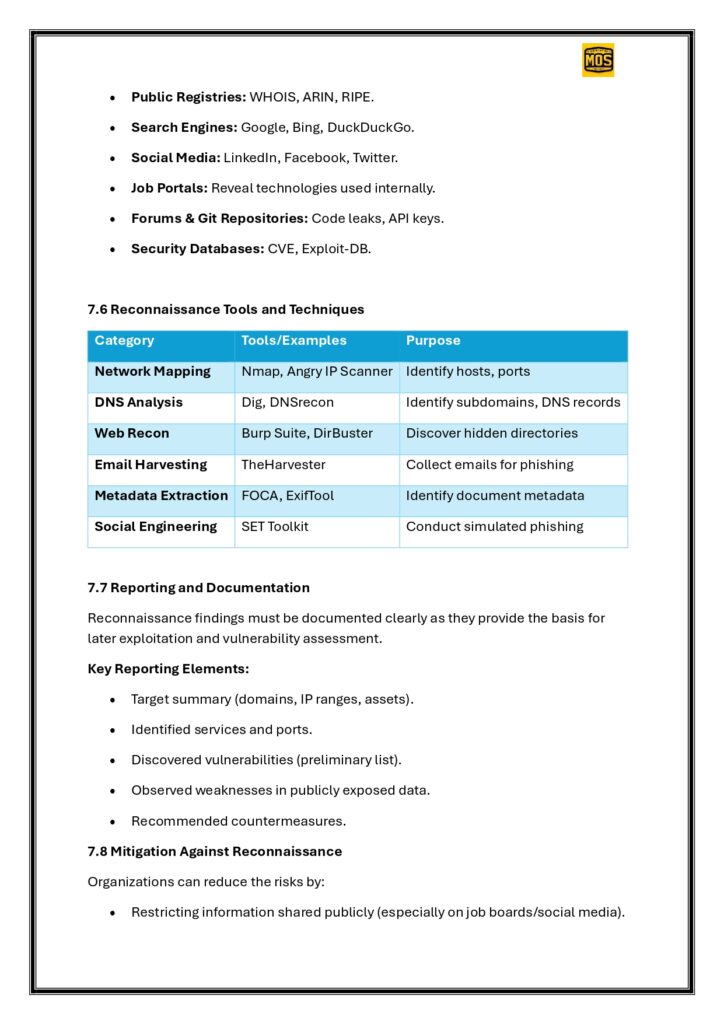
This PDF provides a thorough overview of security assessment methodologies aligned with CISSP standards. It breaks down the principles of risk assessment, outlines testing strategies, and emphasizes the importance of proper documentation.
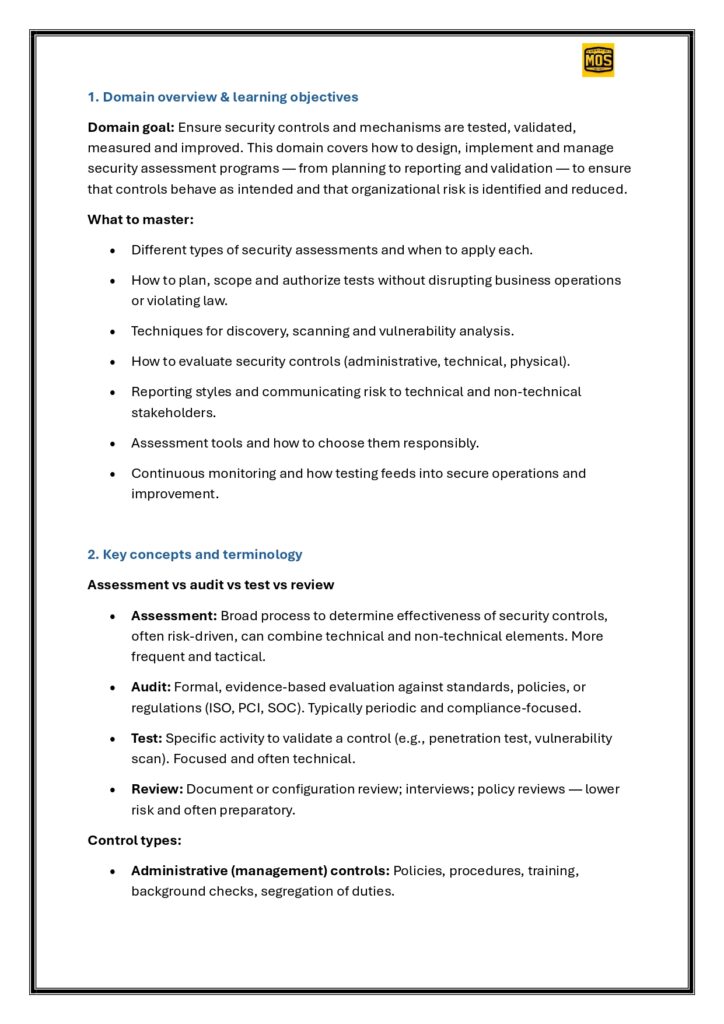
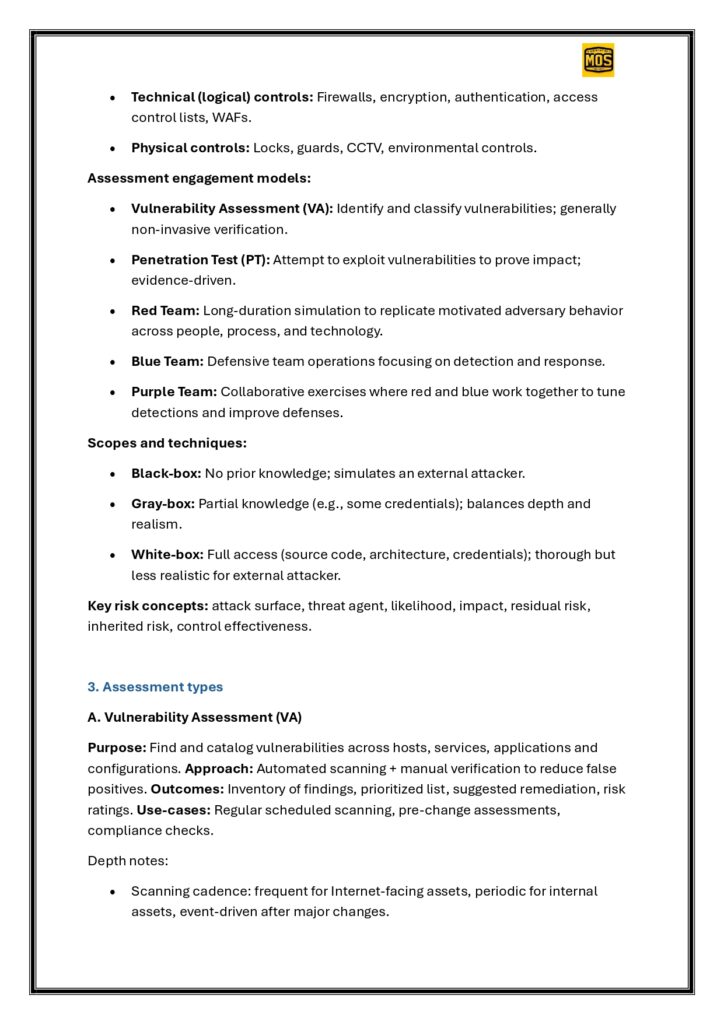
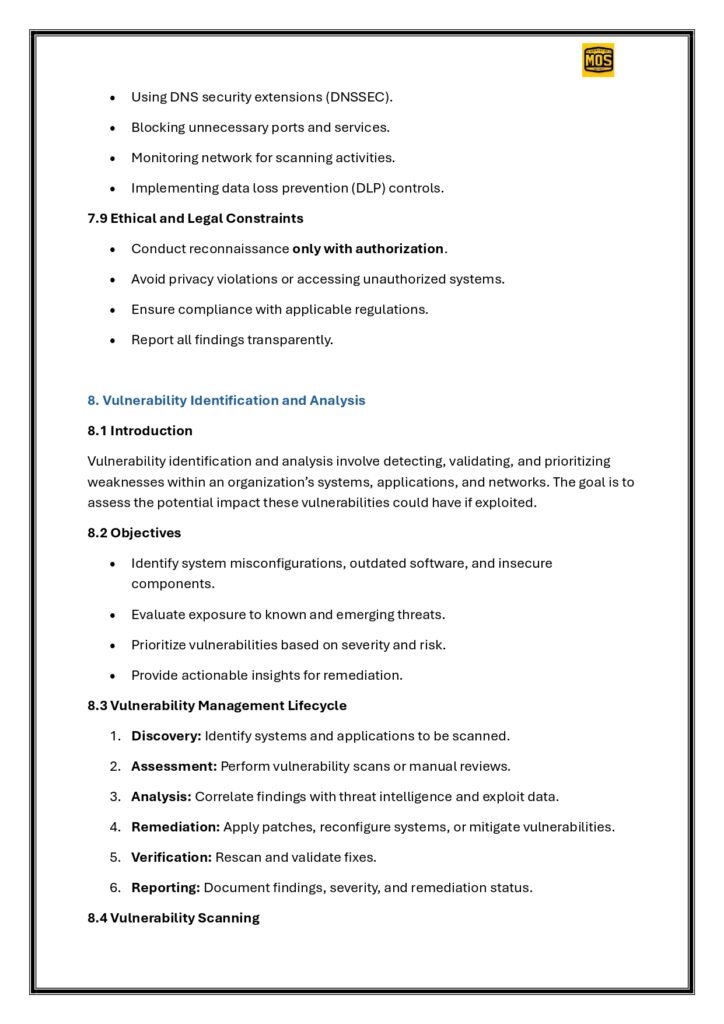
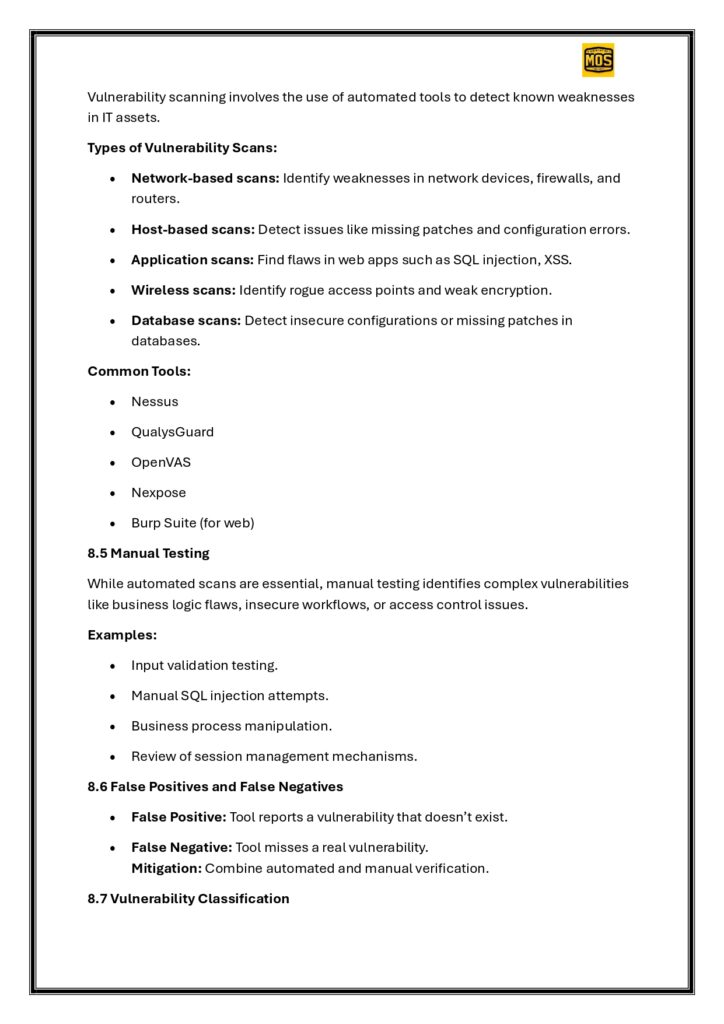
Whether you are a seasoned professional or just starting your journey in cybersecurity, this document will augment your knowledge significantly.
The Content
The document encompasses several key areas including, but not limited to, the role of assessments and testing in securing information systems. It highlights various tools and techniques used for security assessments, thereby aiding practitioners in carrying out their responsibilities effectively. The insights provided within can be indispensable for risk management and compliance efforts.
Table of Contents
- Domain Overview & Learning Objectives
- Key Concepts and Terminology
- Assessment Types
A. Vulnerability Assessment (VA)
B. Penetration Testing (PT)
C. Red Teaming
D. Application Security Testing
E. Configuration/Compliance Assessment & Baseline Validation
F. Social Engineering Tests
G. Physical Security Assessments - Standards, Methodologies, and Frameworks
- Planning and Scoping an Assessment
- Rules of Engagement, Authorization, and Legal Considerations
6.1 Rules of Engagement (ROE)
6.2 Authorization
6.3 Legal Considerations - Reconnaissance and Information Gathering
7.1 Introduction
7.2 Types of Reconnaissance
7.3 Objectives of Reconnaissance
7.4 Information Gathering Techniques
7.5 Data Sources for Reconnaissance
7.6 Reconnaissance Tools and Techniques
7.7 Reporting and Documentation
7.8 Mitigation Against Reconnaissance
7.9 Ethical and Legal Constraints - Vulnerability Identification and Analysis
8.1 Introduction
8.2 Objectives
8.3 Vulnerability Management Lifecycle
8.4 Vulnerability Scanning
8.5 Manual Testing
8.6 False Positives and False Negatives
8.7 Vulnerability Classification
8.8 Risk Prioritization
8.9 Reporting and Metrics
8.10 Continuous Vulnerability Assessment - Penetration Testing Methodologies
9.1 Introduction
9.2 Penetration Testing vs. Vulnerability Assessment
9.3 Phases of Penetration Testing
9.4 Penetration Testing Types
9.5 Penetration Testing Standards & Frameworks
9.6 Tools Used in Penetration Testing
9.7 Post-Testing Activities
9.8 Reporting Best Practices
9.9 Legal and Ethical Aspects
9.10 Continuous Penetration Testing
9.11 Red, Blue, and Purple Teaming - Security Control Testing
10.1 Introduction
10.2 Objectives
10.3 Categories of Controls and Test Approaches
10.4 Control Testing Techniques - Reporting, Communication, Evidence & Remediation Guidance
11.1 Importance of Reporting
11.2 Structure of a Security Assessment Report
11.3 Communication of Results
11.4 Evidence Handling
11.5 Remediation and Re-testing
11.6 Continuous Improvement
11.7 Reporting Best Practices - Post-Engagement Activities
12.1 Objectives
12.2 Key Activities
12.3 Common Pitfalls to Avoid - Lessons Learned and Metrics Analysis
13.1 Purpose
13.2 Lessons Learned Process
13.3 Metrics and Key Performance Indicators (KPIs)
13.4 Reporting Metrics for Management
13.5 Continual Improvement Framework - Documentation and Record Retention
14.1 Types of Documentation
14.2 Retention Policies
14.3 Storage and Security of Records
14.4 Destruction and Disposal
14.5 Benefits of Proper Documentation - Integration with Enterprise Governance and Risk Management
15.1 Objective
15.2 Integration with Governance Frameworks
15.3 Risk Management Linkage
15.4 Communication to Senior Management
15.5 Alignment with Compliance
15.6 Building a Continuous Assurance Model
15.7 Business Benefits of Integration - Maturity Assessment and Optimization
16.1 Purpose
16.2 Maturity Models in Security Testing
16.3 Five Levels of Security Testing Maturity
16.4 Components of a Security Testing Maturity Assessment
16.5 Maturity Assessment Methodology
16.6 Optimization Techniques
16.7 Benefits of Maturity and Optimization - Emerging Trends in Security Testing
17.1 Automation and AI in Security Testing
17.2 DevSecOps and Continuous Security Testing
17.3 Breach and Attack Simulation (BAS)
17.4 Cloud Security Testing
17.5 Attack Surface Management (ASM)
17.6 Zero Trust and Continuous Verification
17.7 Quantum Computing and Cryptographic Resilience
17.8 Privacy and Data Protection Testing
17.9 Human-Centric Testing
17.10 Integration with Threat Hunting and Intelligence
17.11 Future Directions
CISSP Domain 6 Quick Reference
Security Assessment and Testing is Domain 6 of the CISSP exam. Here are the concepts from this PDF that come up most often, in a quick-review format.
Vulnerability Assessment vs. Penetration Test vs. Red Team
| Vulnerability assessment | Penetration test | Red team | |
|---|---|---|---|
| Goal | Find and list weaknesses | Prove weaknesses can be exploited | Test detection and response like a real attacker |
| Depth | Broad, mostly automated | Focused, manual exploitation | Goal-based, stealthy, long-running |
| Output | Prioritized vulnerability list | Exploited paths and impact | Assessment of the blue team’s response |
Testing Approaches You Must Know
- Black box / gray box / white box: testers have no knowledge, partial knowledge, or full knowledge of the target.
- SAST vs. DAST: static testing analyzes source code without running it; dynamic testing attacks the running application.
- Fuzzing: sending large amounts of random or malformed input to find crashes and unexpected behavior.
- Misuse case testing: testing what happens when users deliberately try to abuse a feature.
- Synthetic vs. real user monitoring: scripted transactions versus monitoring what real users actually experience.
SOC Reports at a Glance
| Report | Focus | Audience |
|---|---|---|
| SOC 1 | Controls relevant to financial reporting | Auditors and the customer’s finance team |
| SOC 2 | Security, availability, processing integrity, confidentiality, privacy | Customers and partners (restricted use) |
| SOC 3 | Summary of SOC 2 results | The public |
Type I reports assess control design at a point in time. Type II reports test operating effectiveness over a period (often 6–12 months), so they give more assurance.
Exam Tips for Domain 6
- Written authorization comes first. No testing starts without signed approval and agreed rules of engagement.
- Know who the audience is: technical details go to IT, and risk-based summaries go to senior management.
- Internal, external and third-party audits differ in independence. Third-party audits are the most independent.
- KPIs vs. KRIs: KPIs measure how well security processes perform; KRIs warn that risk is increasing.
Frequently Asked Questions
How much of the CISSP exam is Security Assessment and Testing?
Domain 6 is one of the eight CISSP domains and carries roughly 12% of the exam in the current outline. Check the ISC2 exam outline for the latest weights.
Is this PDF useful outside the CISSP exam?
Yes. Planning, scoping, rules of engagement, reporting and maturity models are everyday topics for security analysts, auditors and penetration testers.
Why the Document?
This PDF is an essential tool for professionals aiming to deepen their understanding of security assessments and testing frameworks. Its practical approach, combined with real-world examples, makes it a helpful guide that bridges theory with practice. With comprehensive content grounded in the core principles of CISSP, readers can apply these concepts in real-world scenarios to improve their organizations’ security posture.
Conclusion
In summary, the CISSP Security Assessment and Testing PDF is an invaluable asset for anyone in the cybersecurity realm. It not only provides critical knowledge but also serves as a reference point for continuous learning and application of security practices.
Download from Below Link
Ready to enhance your cybersecurity skills? Download the CISSP Security Assessment and Testing PDF using the link below:
Download CISSP Security Assessment and Testing PDF
Related Free Cybersecurity Resources
- CISSP Exam Preparation PDF: Your Path to Success
- CISSP Cheat Sheet Series (PDF)
- CISSP Exam Study Guide PDF
- CISSP Study Guide PDF
- Introduction to IoT Security (PDF)
- CompTIA Security+ Study Guide PDF